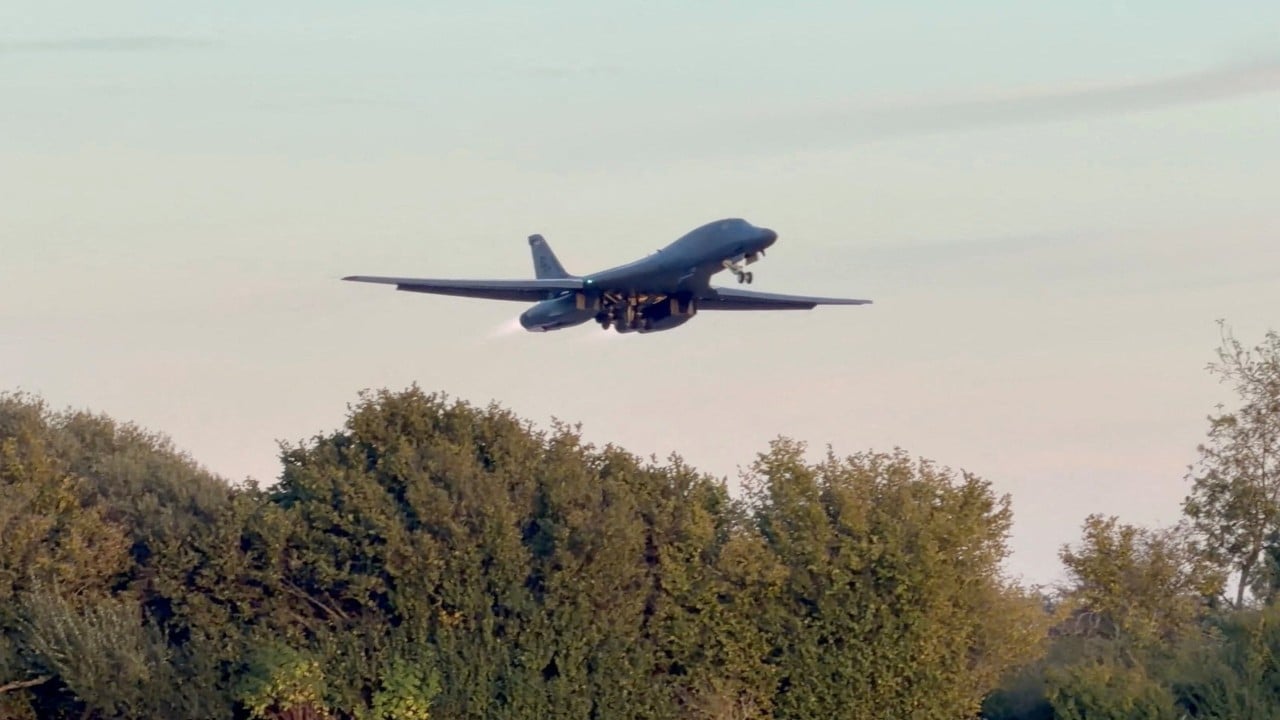
Two men get charged in the UK with assisting Iranian intelligence over an incident at a Royal Air Force base, and the mainstream press immediately reaches for its favorite dusty playbook. They frame it as a high-stakes Cold War thriller. Shadows by the perimeter fence. Trench coats near the runway. A triumphant victory for domestic security services catching foreign agents red-handed.
That narrative is dangerously comforting, and it misses the entire point.
Treating physical perimeter breaches around RAF installations as isolated espionage wins ignores the massive structural rot in how Western militaries secure their infrastructure. When foreign intelligence services—specifically Tehran's Ministry of Intelligence and Security (MOIS) or the Islamic Revolutionary Guard Corps (IRGC)—run operations near British airfields, they rarely care about stealing blueprints off a desk anymore. They are exploiting a wide-open seam between physical security, commercial data brokers, and outsourced base logistics.
I have spent over a decade auditing physical-digital convergence risks for defense contractors and critical infrastructure operators across Europe. I have watched agencies burn millions of pounds upgrading biometric turnstiles at the front gate while leaving the contractors who empty the trash bins, fix the HVAC systems, and deliver catering completely unvetted beyond a basic criminal record check.
If you are celebrating these charges as proof that the system works, you are looking at the symptom while the infection spreads unchecked.
The Myth of the High-Tech Fortress
The standard reporting around UK National Security Act prosecutions relies on an outdated assumption. The public imagines RAF bases—whether hubs like RAF Akrotiri, RAF Brize Norton, or joint intelligence facilities like RAF Menwith Hill—as impenetrable citadels guarded by cutting-edge surveillance grids and elite patrols.
They are not. Modern military installations operate less like medieval castles and more like small, poorly zoned industrial parks.
To keep defense budgets from imploding, the UK Ministry of Defence (MOD) outsourced almost every non-combat function decades ago. Private facilities management conglomerates handle maintenance. Third-party logistics firms move equipment. Local subcontractors patch the tarmac.
This creates an enormous attack surface that requires zero tradecraft to penetrate. An adversarial intelligence officer does not need to recruit a disgruntled squadron leader with Top Secret clearance. They just need to spot a financially stressed subcontractor, a gig-economy delivery driver, or an activist willing to take cash to point a camera at a flight line.
The National Security Act 2023 Reality Check
When Parliament passed the National Security Act 2023, replacing the archaic Official Secrets Act 1911, the goal was clear. Prosecutors needed modern tools to charge individuals for "assisting a foreign intelligence service" without having to prove they handed over classified documents marked "SECRET."
Under Section 3 of the Act, simply gathering routine, unclassified information—like flight schedules, vehicle license plates, or perimeter patrol timings—becomes a severe criminal offense if done on behalf of a foreign power.
Law enforcement loves this statute because it lowers the evidentiary bar for arrests. Yet from an operational security standpoint, relying on post-incident prosecutions is an admission of failure. By the time the Crown Prosecution Service files charges over an air base incident, the reconnaissance has already happened. The photos have already been transmitted over encrypted messaging apps. The pattern-of-life data is already sitting on a server in Tehran.
How Foreign Intelligence Actually Maps Military Bases
To understand why these incidents keep happening, you have to stop thinking like a counterintelligence bureaucrat and start thinking like a targeter.
Suppose you are running an intelligence desk tasked with monitoring UK military support for operations in the Middle East. You do not care about the aerodynamics of an F-35B Lightning II. You can read about that on Wikipedia. You care about logistics and tempo.
You want to know:
- Which transport aircraft are taking off at 03:00?
- What cargo pallets are being loaded onto C-17 Globemasters?
- Which contractors are entering the base with specialized munitions handling gear?
- How fast do Quick Reaction Alert (QRA) crews respond when an alarm trips at the south gate?
You cannot get that data from a commercial satellite image taken once every 48 hours. You need eyes on the ground.
The Proxy Network Model
Iranian intelligence has perfected the art of the disposable proxy. Unlike Russian services, which historically favored deeply embedded illegals or recruited ideological insiders, Tehran routinely uses criminal networks, local opportunists, and low-level operatives to conduct physical surveillance and harassment across Europe.
MI5 Director General Ken McCallum has repeatedly warned about this exact shift. Speaking publicly about state threats in the UK, McCallum highlighted how hostile states—Iran prominent among them—increasingly subcontract their dirty work to private criminals and unwitting locals to maintain plausible deniability and insulate their own officers from arrest.
When two men are charged over an incident at an RAF base, look closely at their profiles. Are they career intelligence officers trained in covert communications and dead drops? Almost never. They are usually local assets—cutouts paid a few thousand pounds to take photographs, fly a commercial drone near restricted airspace, or test perimeter response times.
Catching the cutout does nothing to degrade the network running them. It is the intelligence equivalent of arresting a street-level drug runner while the cartel boss sits untouched in another jurisdiction.
The Open-Source Blind Spot Nobody Mentions
Here is the uncomfortable truth that defense officials hate admitting. Even if you locked down every fence around every RAF base tomorrow, foreign adversaries would still know almost everything happening inside them.
Why? Because military personnel and base contractors leak operational security every single day through their smartphones.
Commercial Telemetry and ADINT
You do not need a spy in the bushes when you have Advertising Intelligence (ADINT).
Every time a soldier, civilian technician, or delivery driver walks onto an RAF base with a weather app, a fitness tracker, or a free mobile game installed on their personal phone, that device broadcasts its unique Mobile Advertising ID (MAID) alongside precise GPS coordinates.
Commercial data brokers harvest this telemetry by the billions and sell it on the open market. Any shell company with a modest budget can buy bulk location data, draw a geofence around a British airfield, and watch the anonymized dots move from the barracks to the hangars, and then follow those exact same dots back to their home addresses in nearby towns.
Imagine a scenario where an adversarial analyst wants to identify every engineer working on a specific electronic warfare squadron. They do not need to infiltrate the base. They simply purchase six months of historical location telemetry for the hangar area, filter out devices that only visit once, and isolate the phones that spend forty hours a week inside that specific building. Then they trace those devices home at night, cross-reference the addresses with public voter rolls or property records, and suddenly they have a complete roster of names, faces, and financial vulnerabilities.
Against that kind of industrial-scale data harvesting, arresting two guys near a fence looks like theater.
Dismantling the Common Misconceptions
Public discourse around domestic espionage is riddled with bad assumptions. If we want actual security instead of security theater, we have to dismantle the questions people usually ask.
"Why didn't base security stop them before they got close?"
Because public roads run directly alongside almost every major airfield in the UK. Plane spotting is a massive, completely legal hobby in Britain. Hundreds of enthusiasts stand outside RAF bases every week with telephoto lenses and radio scanners, logging tail numbers and posting them on aviation forums.
Base security cannot arrest everyone with a camera standing on a public footpath. Adversaries exploit this cultural norm deliberately. A hostile operative standing near the perimeter fence looks identical to an aviation geek until they cross a specific legal or physical line. By the time military police distinguish between a hobbyist and a reconnaissance asset, the visual intelligence has already been captured.
"Does charging suspects under the National Security Act deter Tehran?"
No. Deterrence only works when the cost of failure exceeds the value of the objective, and when that cost is borne by the decision-maker.
Tehran pays zero operational price when two disposable assets in the UK get arrested. The IRGC loses no trained officers. Their diplomatic cover remains intact if the operation was run remotely via encrypted platforms. From their perspective, burning two low-level assets to gain tactical awareness of UK airlift operations—or simply to force British security services to burn thousands of investigative hours—is a massive return on investment.
"Should the UK ban all drones and photography near military sites?"
You can pass all the bans you want, and they will stop precisely zero determined adversaries. Geofencing on commercial drones is trivial to bypass with open-source firmware patches available on GitHub in ten minutes. Banning photography from public roads simply criminalizes hobbyists while hostile operatives switch to concealed body-worn cameras or dashboard mounts on parked vans.
Laws do not stop bullets, and statutory instruments do not block optics.
What Real Base Counterintelligence Looks Like
If the UK Ministry of Defence and allied militaries want to stop bleeding operational intelligence, they have to abandon the perimeter-centric mindset. Securing a modern military base requires treating it as an information environment, not just a piece of real estate.
1. Kill Personal Devices Inside Sensitive Zones
The single highest-leverage move any military installation can make tomorrow is enforcing a zero-tolerance policy on personal smartphones inside operational perimeters—not just inside SCIFs (Sensitive Compartmented Information Facilities), but across the entire flight line and logistics hub.
Provide issued, locked-down communication devices for base personnel, and require personal phones to be left in Faraday-shielded lockers at the main gate. Until you sever the commercial telemetry pipeline, your perimeter fence is an illusion.
2. Audit the Supply Chain Down to the Sub-Tier
Security vetting currently focuses on who holds a clearance. It needs to focus on access.
A cleaner with unescorted access to an administrative building or a contractor servicing backup generators poses a higher physical espionage risk than a junior officer who rarely leaves their desk. Every third-party vendor operating on an RAF base should undergo continuous background monitoring—specifically tracking sudden financial distress, unexplained foreign travel, and online radicalization—rather than a one-off check every five years.
3. Deploy Active Counter-Surveillance, Not Passive Cameras
Passive CCTV records crimes so prosecutors can play the footage in court six months later. Active counter-surveillance disrupts the collection cycle in real time.
Base security units need dedicated plainclothes counter-reconnaissance teams operating outside the wire. Their job is to identify anomalous patterns—vehicles parked repeatedly along approach paths, individuals loitering near contractor entrances, or unusual RF emissions—and intervene aggressively before data leaves the area.
4. Poison the OSINT Well
If adversaries are using open-source data and visual observation to track deployments, stop giving them clean signals.
Vary flight schedules unpredictably. Use decoy cargo movements. Restrict the release of routine unit deployment announcements on official MOD social media channels. Make the adversary work ten times harder to verify whether a transport flight is carrying humanitarian aid, spare parts, or precision munitions.
The Hard Truth About Defense Vulnerability
There is a downside to this approach, and it is the reason politicians avoid it. Real operational security is expensive, inconvenient, and deeply unpopular with the people who have to live under it.
Banning personal phones on bases creates friction for service members trying to stay in touch with their families. Aggressive vetting of local contractors slows down base maintenance and drives up procurement costs. Treating the perimeter outside the fence as an active intelligence zone invites civil liberties pushback from local residents and aviation enthusiasts.
It is much easier for the government to keep the status quo, wait for an incident to happen, arrest the low-level operatives involved, and issue a press release praising the vigilance of the security services.
That approach makes for great headlines. It gives the public the comforting illusion that the borders are tight and the bad guys are behind bars.
Meanwhile, the data brokers are still selling the GPS coordinates of every airman on base, the subcontractors are still driving through the gates with unvetted phones in their pockets, and the intelligence services in Tehran are already recruiting the next two guys to stand by the fence.